But over time, those changes alter how your application behaves. How data moves. How users authenticate.
If it changes, test it.
New endpoint exposed
Exposure shifts quietly
CONTINUOUS
More than a snapshot
Application testing is often treated as a single event. A report at a specific moment in time. But your application doesn't stop changing after that.
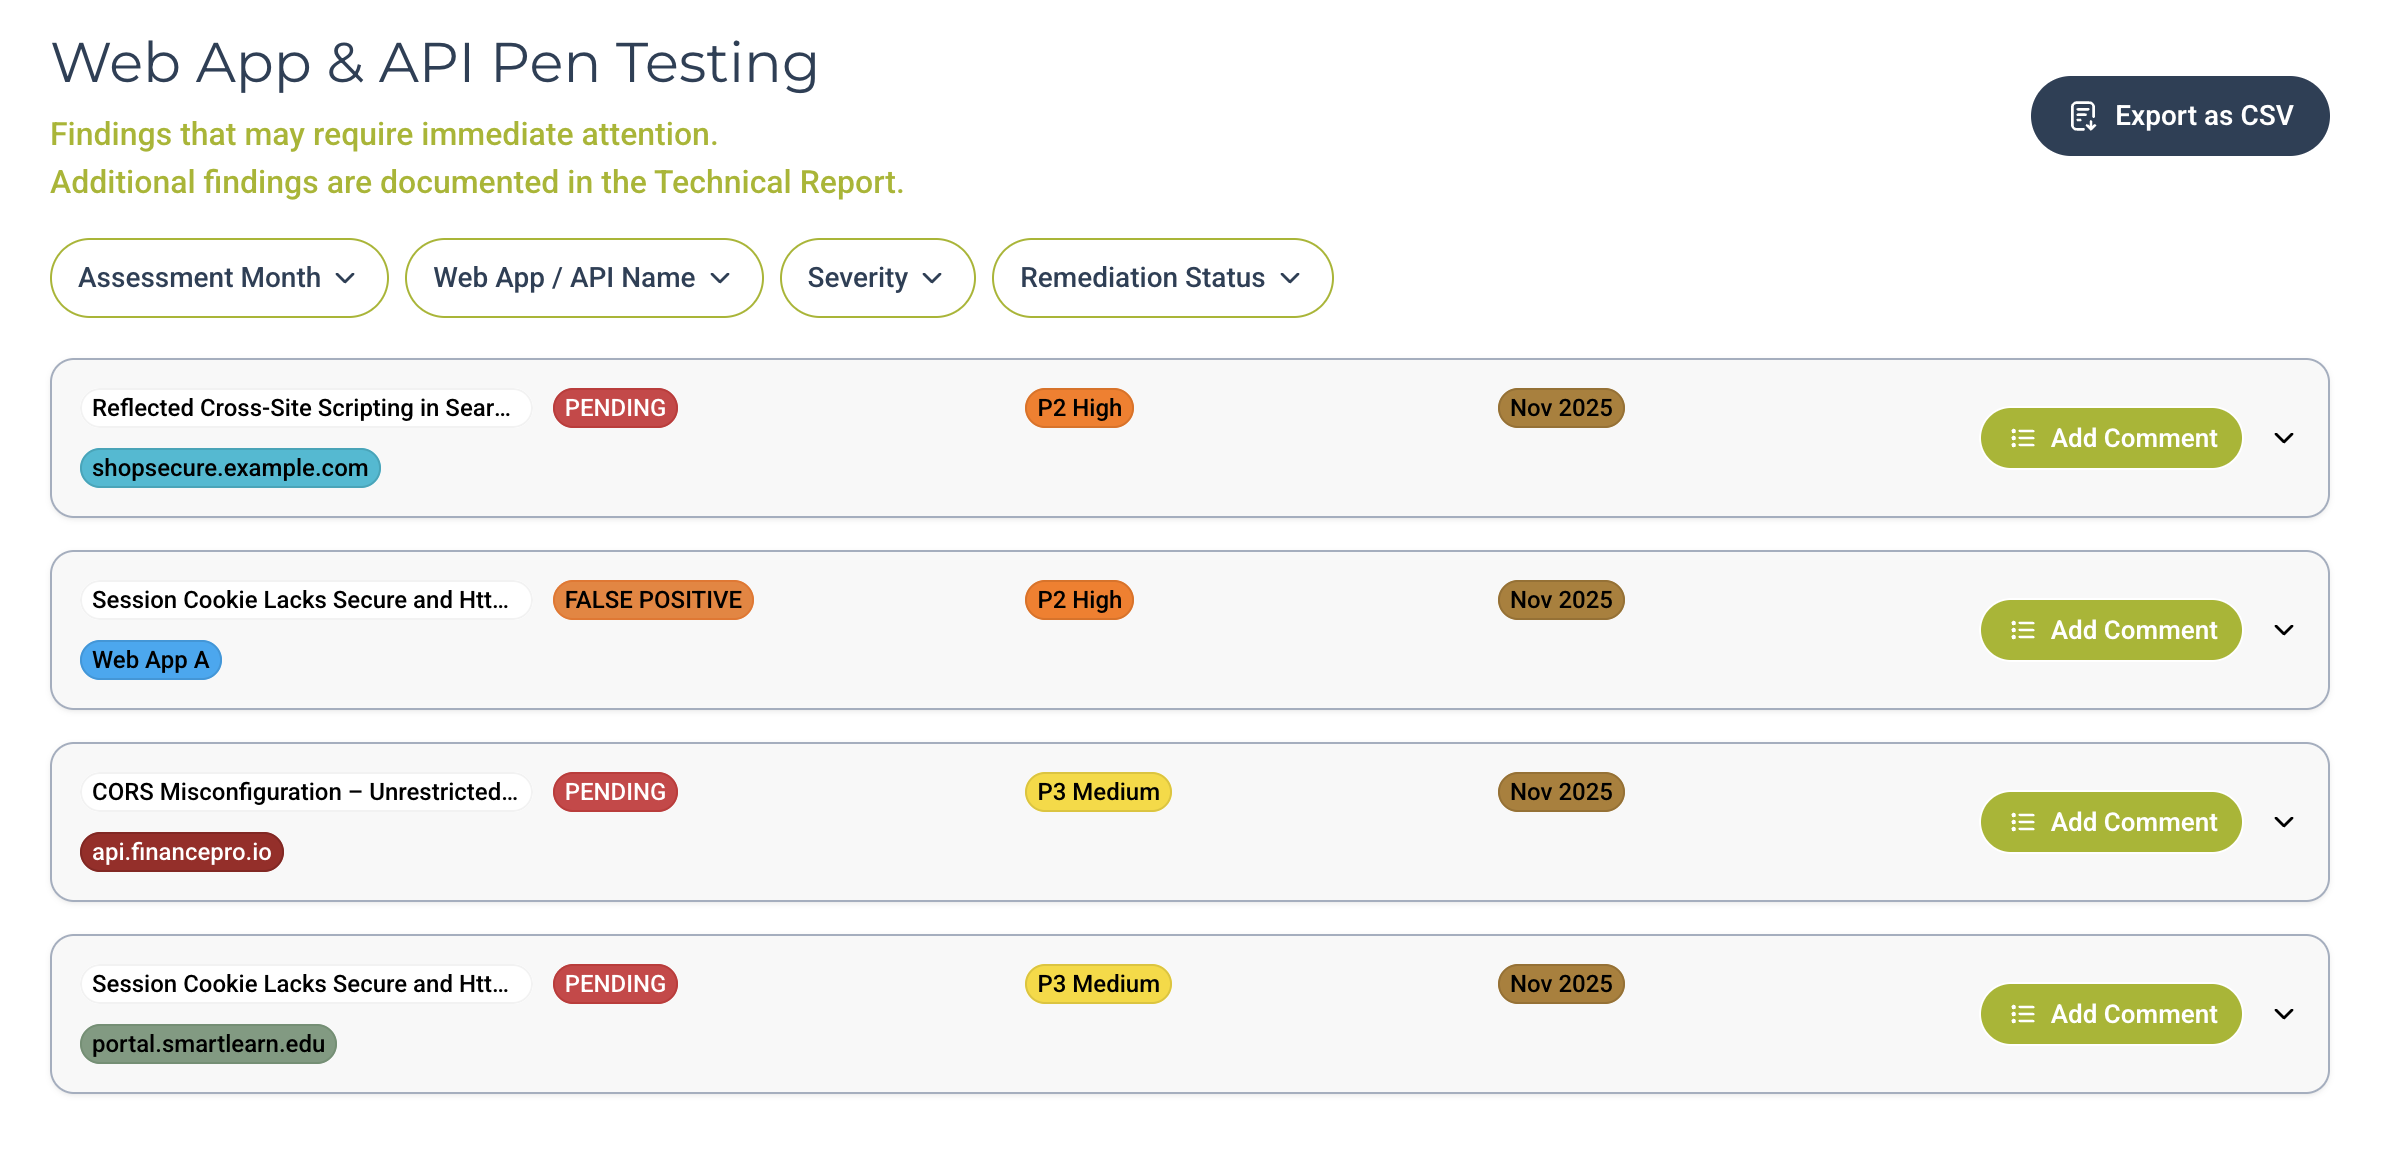
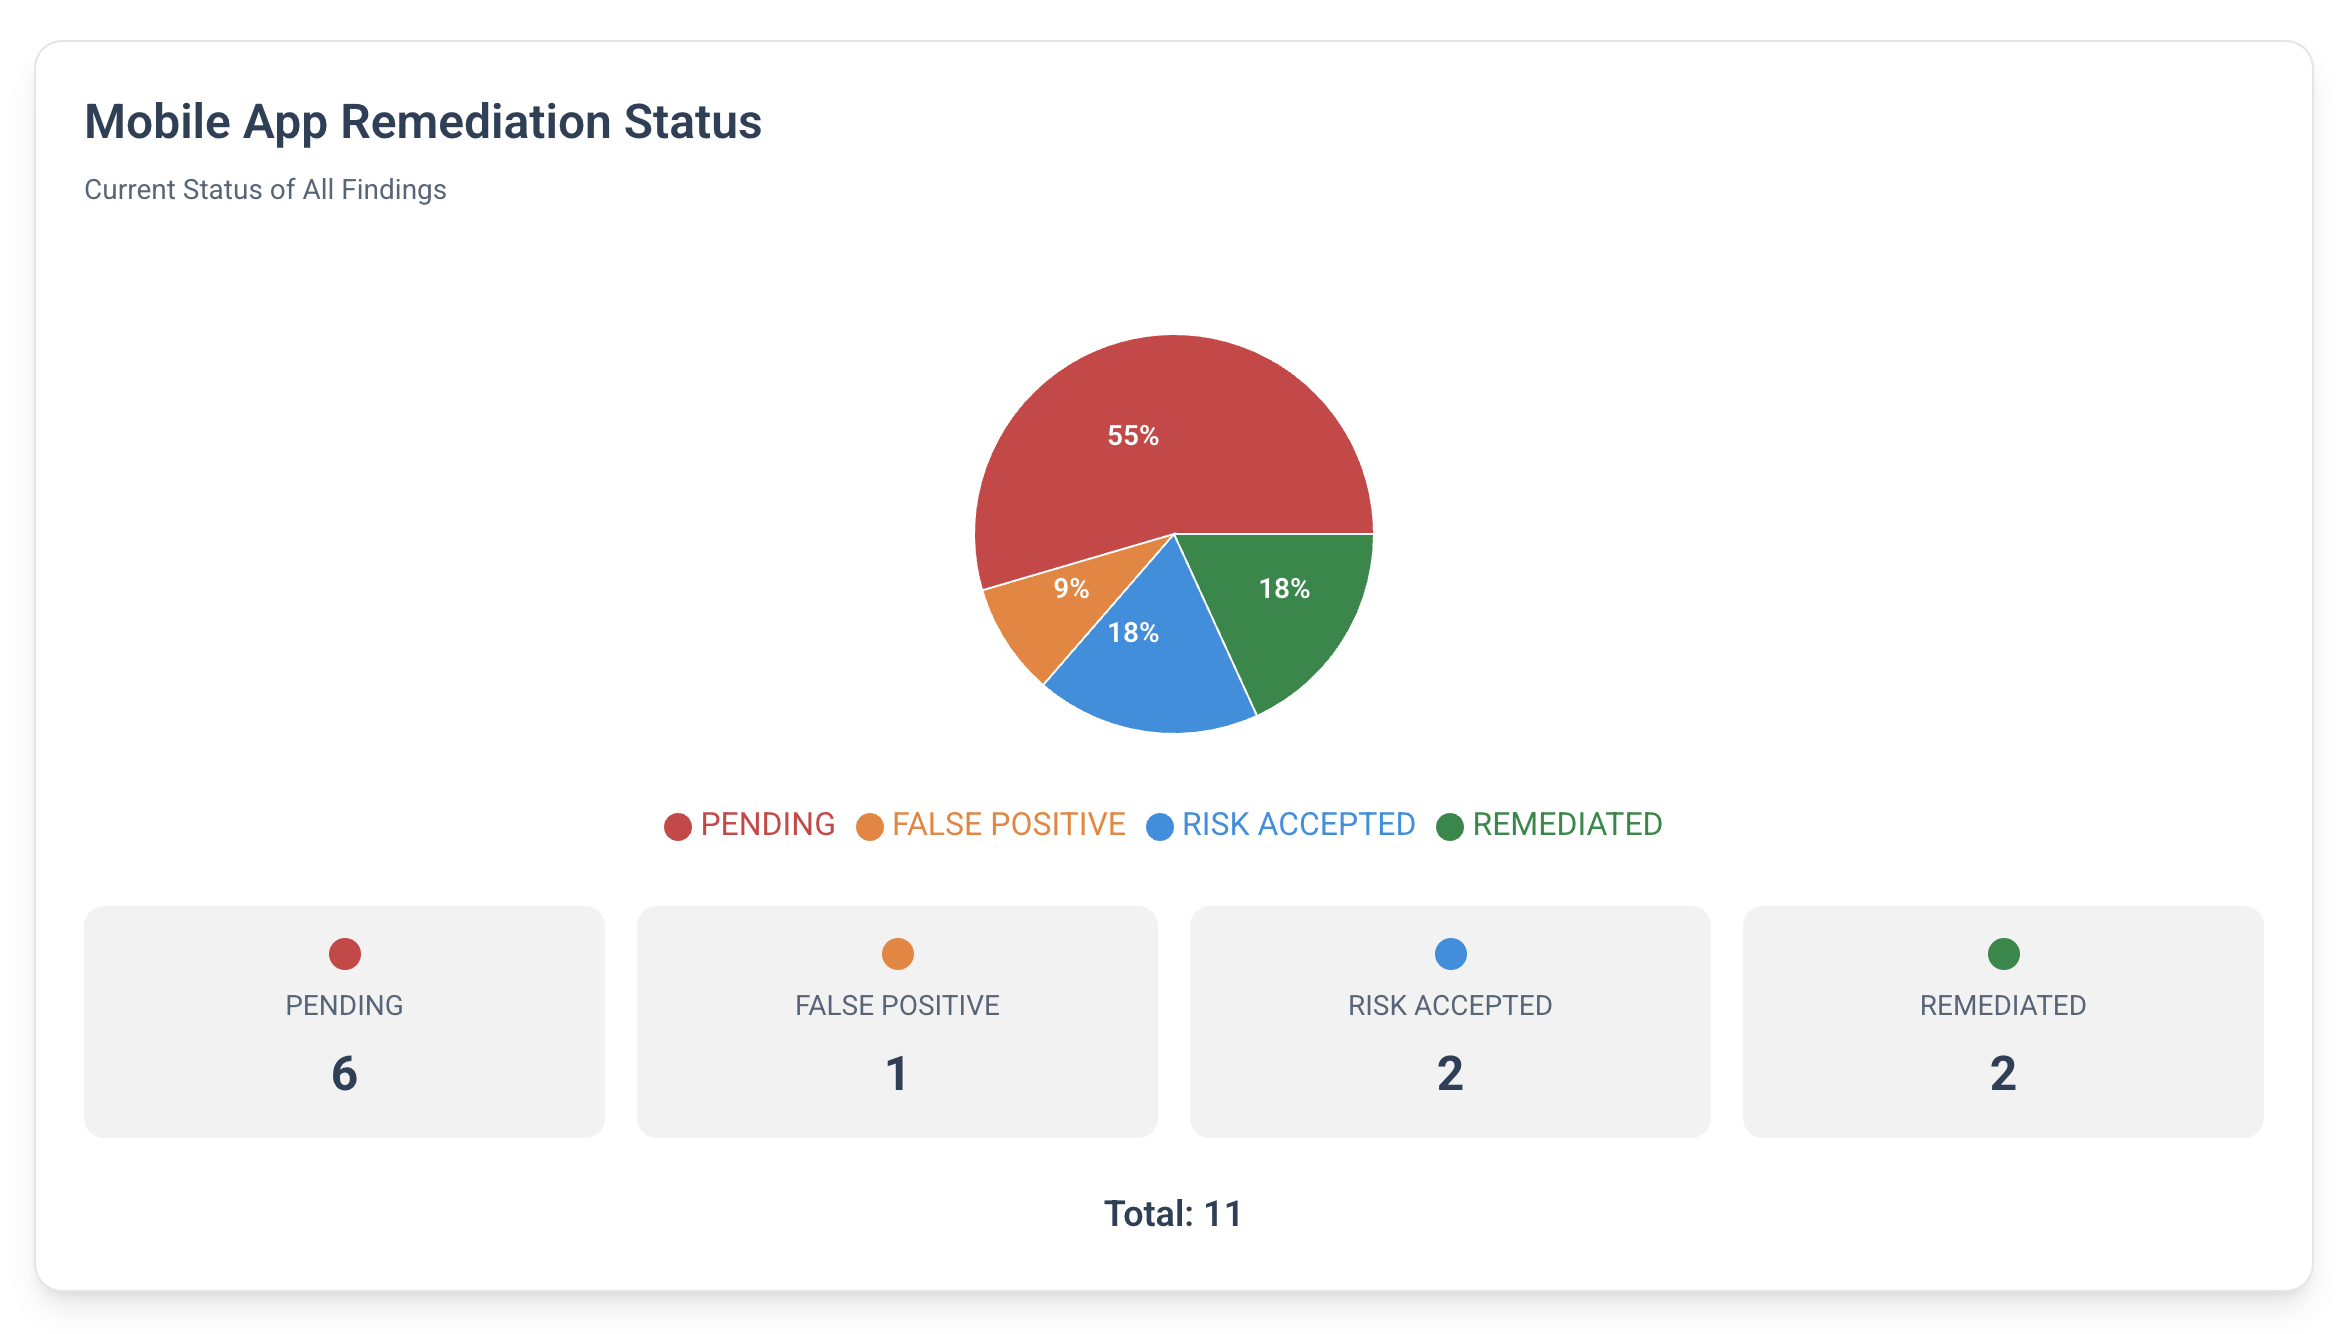
You start to see
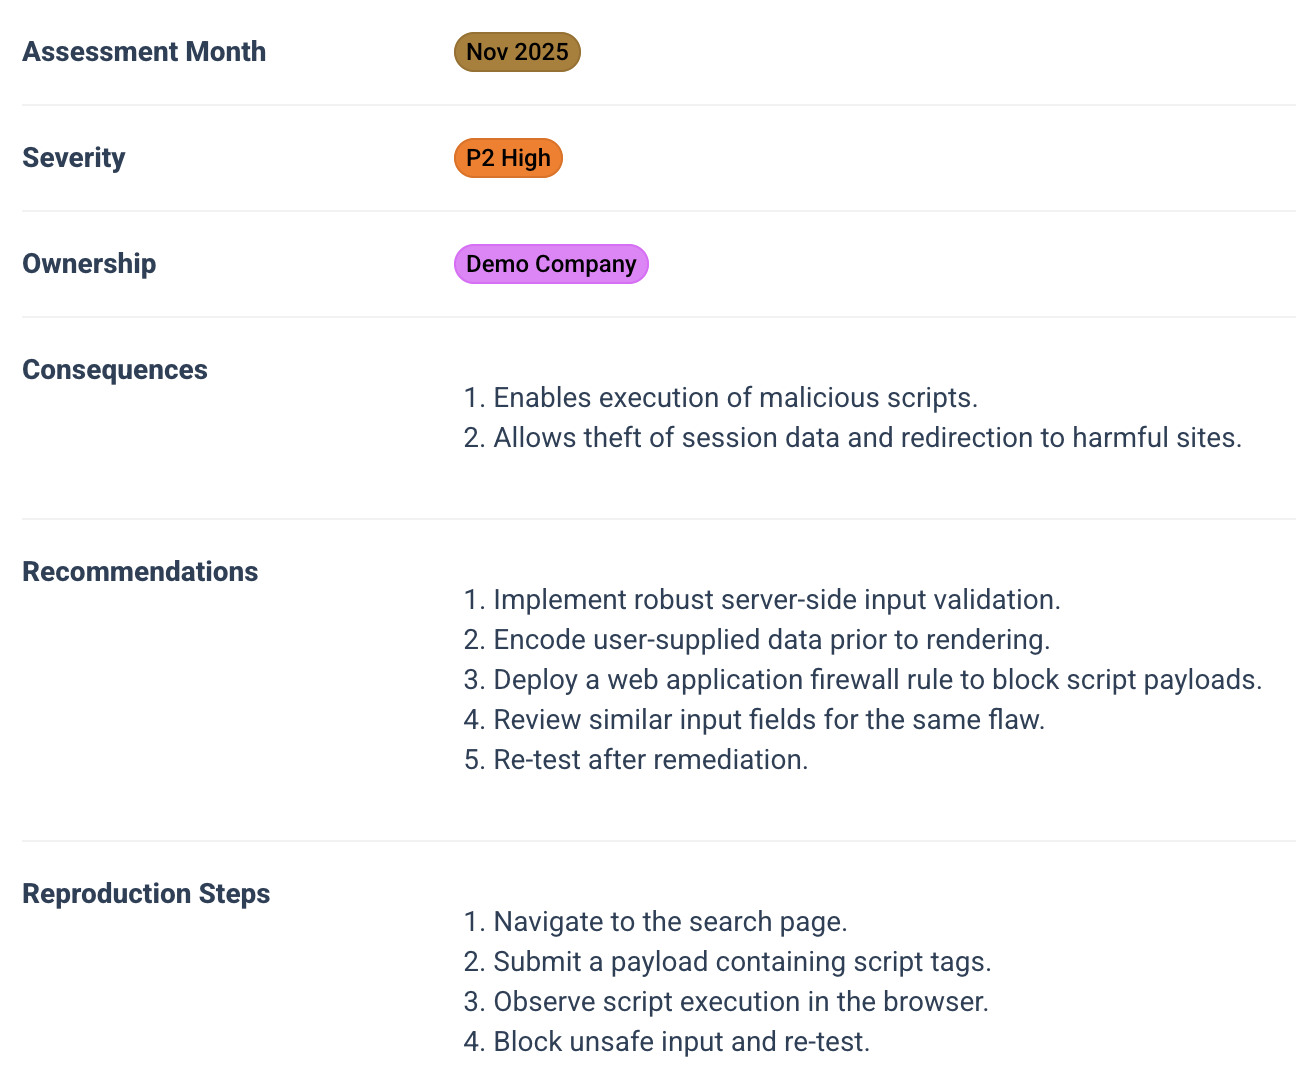
What's new. What's shifted.
What's been resolved.
What needs attention now.
HOW WE WORK
Risk, understood
Findings are prioritised based on real-world impact. Attention goes where it genuinely matters.
Your team gets practical guidance they can act on. And as your application changes, testing keeps pace.
Not a one-off exercise. A consistent view of how risk moves within your application.
LIVE VISIBILITY, NOT JUST A REPORT
Security you can actually see
Testing aligns with how your application evolves.
Scope is agreed in advance, based on what matters most.
Findings are prioritised based on real impact.
The focus is not volume. It's sustained understanding.
WHO IT'S FOR
Designed for organisations where applications matter
Organisations where applications are central to how you operate.
Where customer-facing systems, APIs or sensitive data are involved.
Where application risk needs to be understood, not assumed.
Findings that stay current
Not a snapshot from last quarter.
Prioritised, not just listed
See what needs attention. What can wait.
All in one place
Live in digitalCISO. Always accessible.
If your environment also includes network infrastructure, we can cover that too.