SERVICE LED, PLATFORM SUPPORTED

When did you last check whether your controls still hold up?

Governance, Risk & Compliance Services

Clarity. Not just compliance.

See Where You Stand
Sound familiar?

Getting compliant is one thing. Staying compliant is another.

Compliance frameworks give you a solid baseline. Cyber Essentials, ISO 27001, PCI DSS. Achieving certification directly improves your security posture.

But your business keeps moving. New systems, new processes, new risks.

The question isn't whether your framework matters. It's whether your last assessment still reflects where you are today.

Continuous GRC gives you the structure to keep pace.
Last Assessed: 14 months ago
Every six months, we run a gap analysis against your chosen framework.

We drive the assessment. You bring in the right people from across your business.

Findings, evidence, and an audit-ready report. All captured in the platform and ready to export.

Then we run it again.

So progress is measured, not assumed.
SIX-MONTHLY. NOT ONCE AND FORGOTTEN.

A structured assessment that actually keeps pace

FRAMEWORK

The right framework for your business, not ours

Not every organisation needs the same framework. Some are working towards certification for the first time. Some are renewing. Some just want a structured view of where they stand.

We'll work to whichever framework fits your business and your obligations.

Cyber Essentials
Cyber Essentials Plus
ISO/IEC 27001
ISO/IEC 42001
NIST CSF 2.0
PCI DSS

YOUR GAPS, IN ONE PLACE

Your findings don't disappear

Your gap analysis lives in our GRC platform.
‍
Your findings. Your evidence. Your progress.
All structured. All accessible. All yours.
‍
Results also surface in digitalCISO, our cyber risk hub.
‍
So your team always has a current view of where things stand.
‍
Not just a report from six months ago.
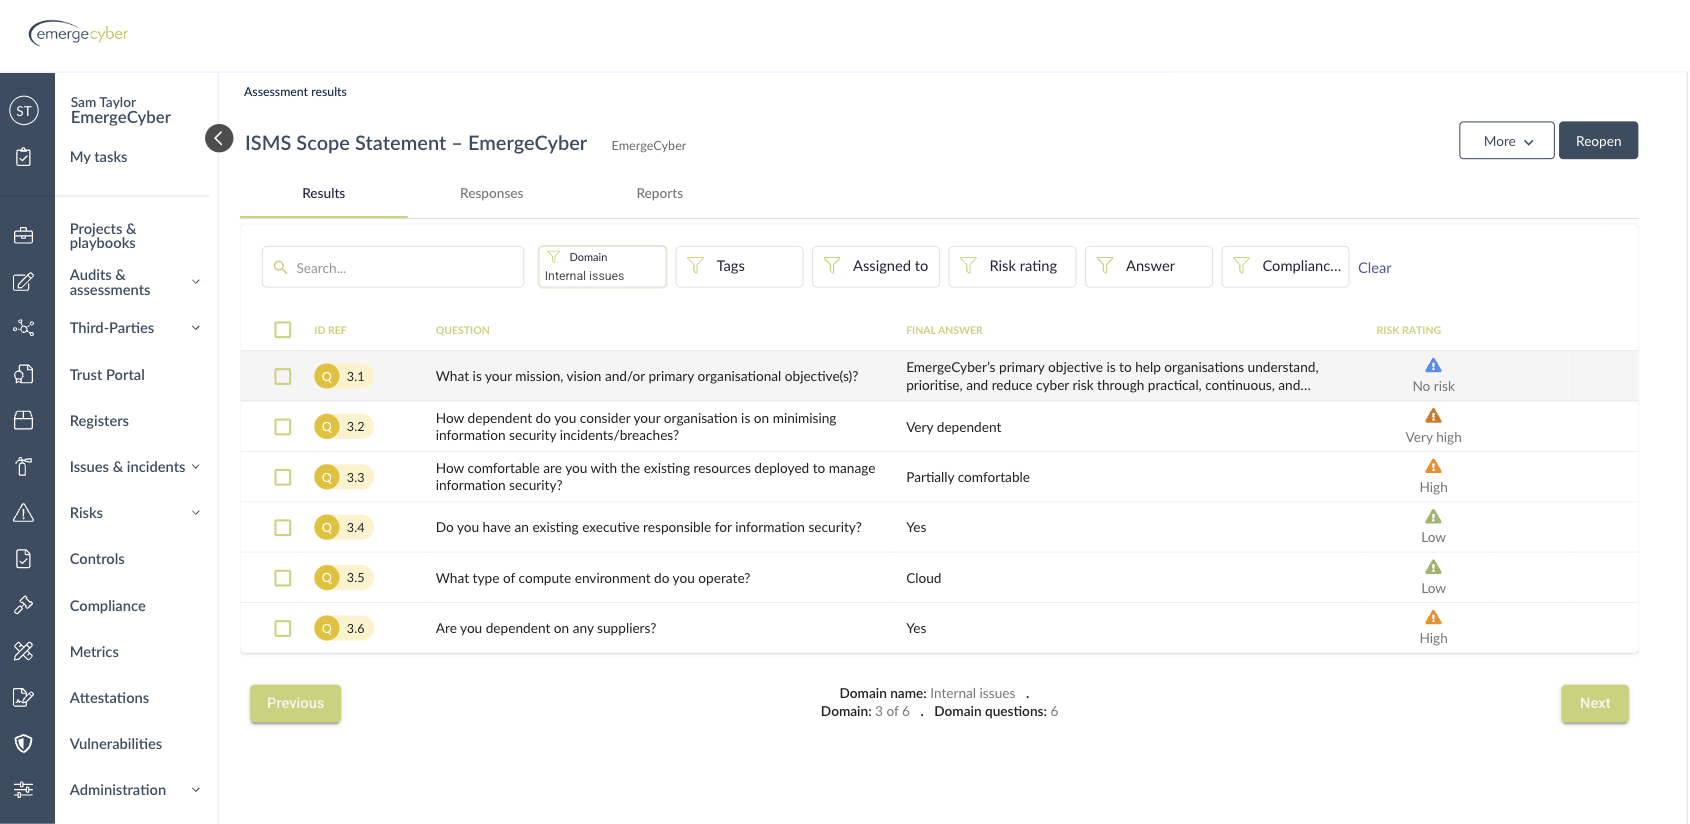
Example GRC assessment results in digitalCISO
Compliance gaps don't tell you what's exploitable.
Technical findings don't tell you what matters to the business.
Separately, they leave gaps.
Together, they clarify.
WHEN SERVICES COMBINE

Three services. One picture.

Standalone GRC shows you where you fall short on paper.
‍
Pen testing shows you what can be exploited in practice.

On their own, both leave gaps.

When you combine GRC with continuous pen testing, those gaps close.

You stop looking at fragments and start seeing the full picture.

We show you what matters and what to do next.

Every month.
CYBER RISK STATUS ATTESTATION

One view of your risk. Every month.

When you bring GRC and continuous testing together, something changes.
‍
You're no longer working across separate reports, findings, and frameworks.
‍
Each month, everything comes together in one view.
‍
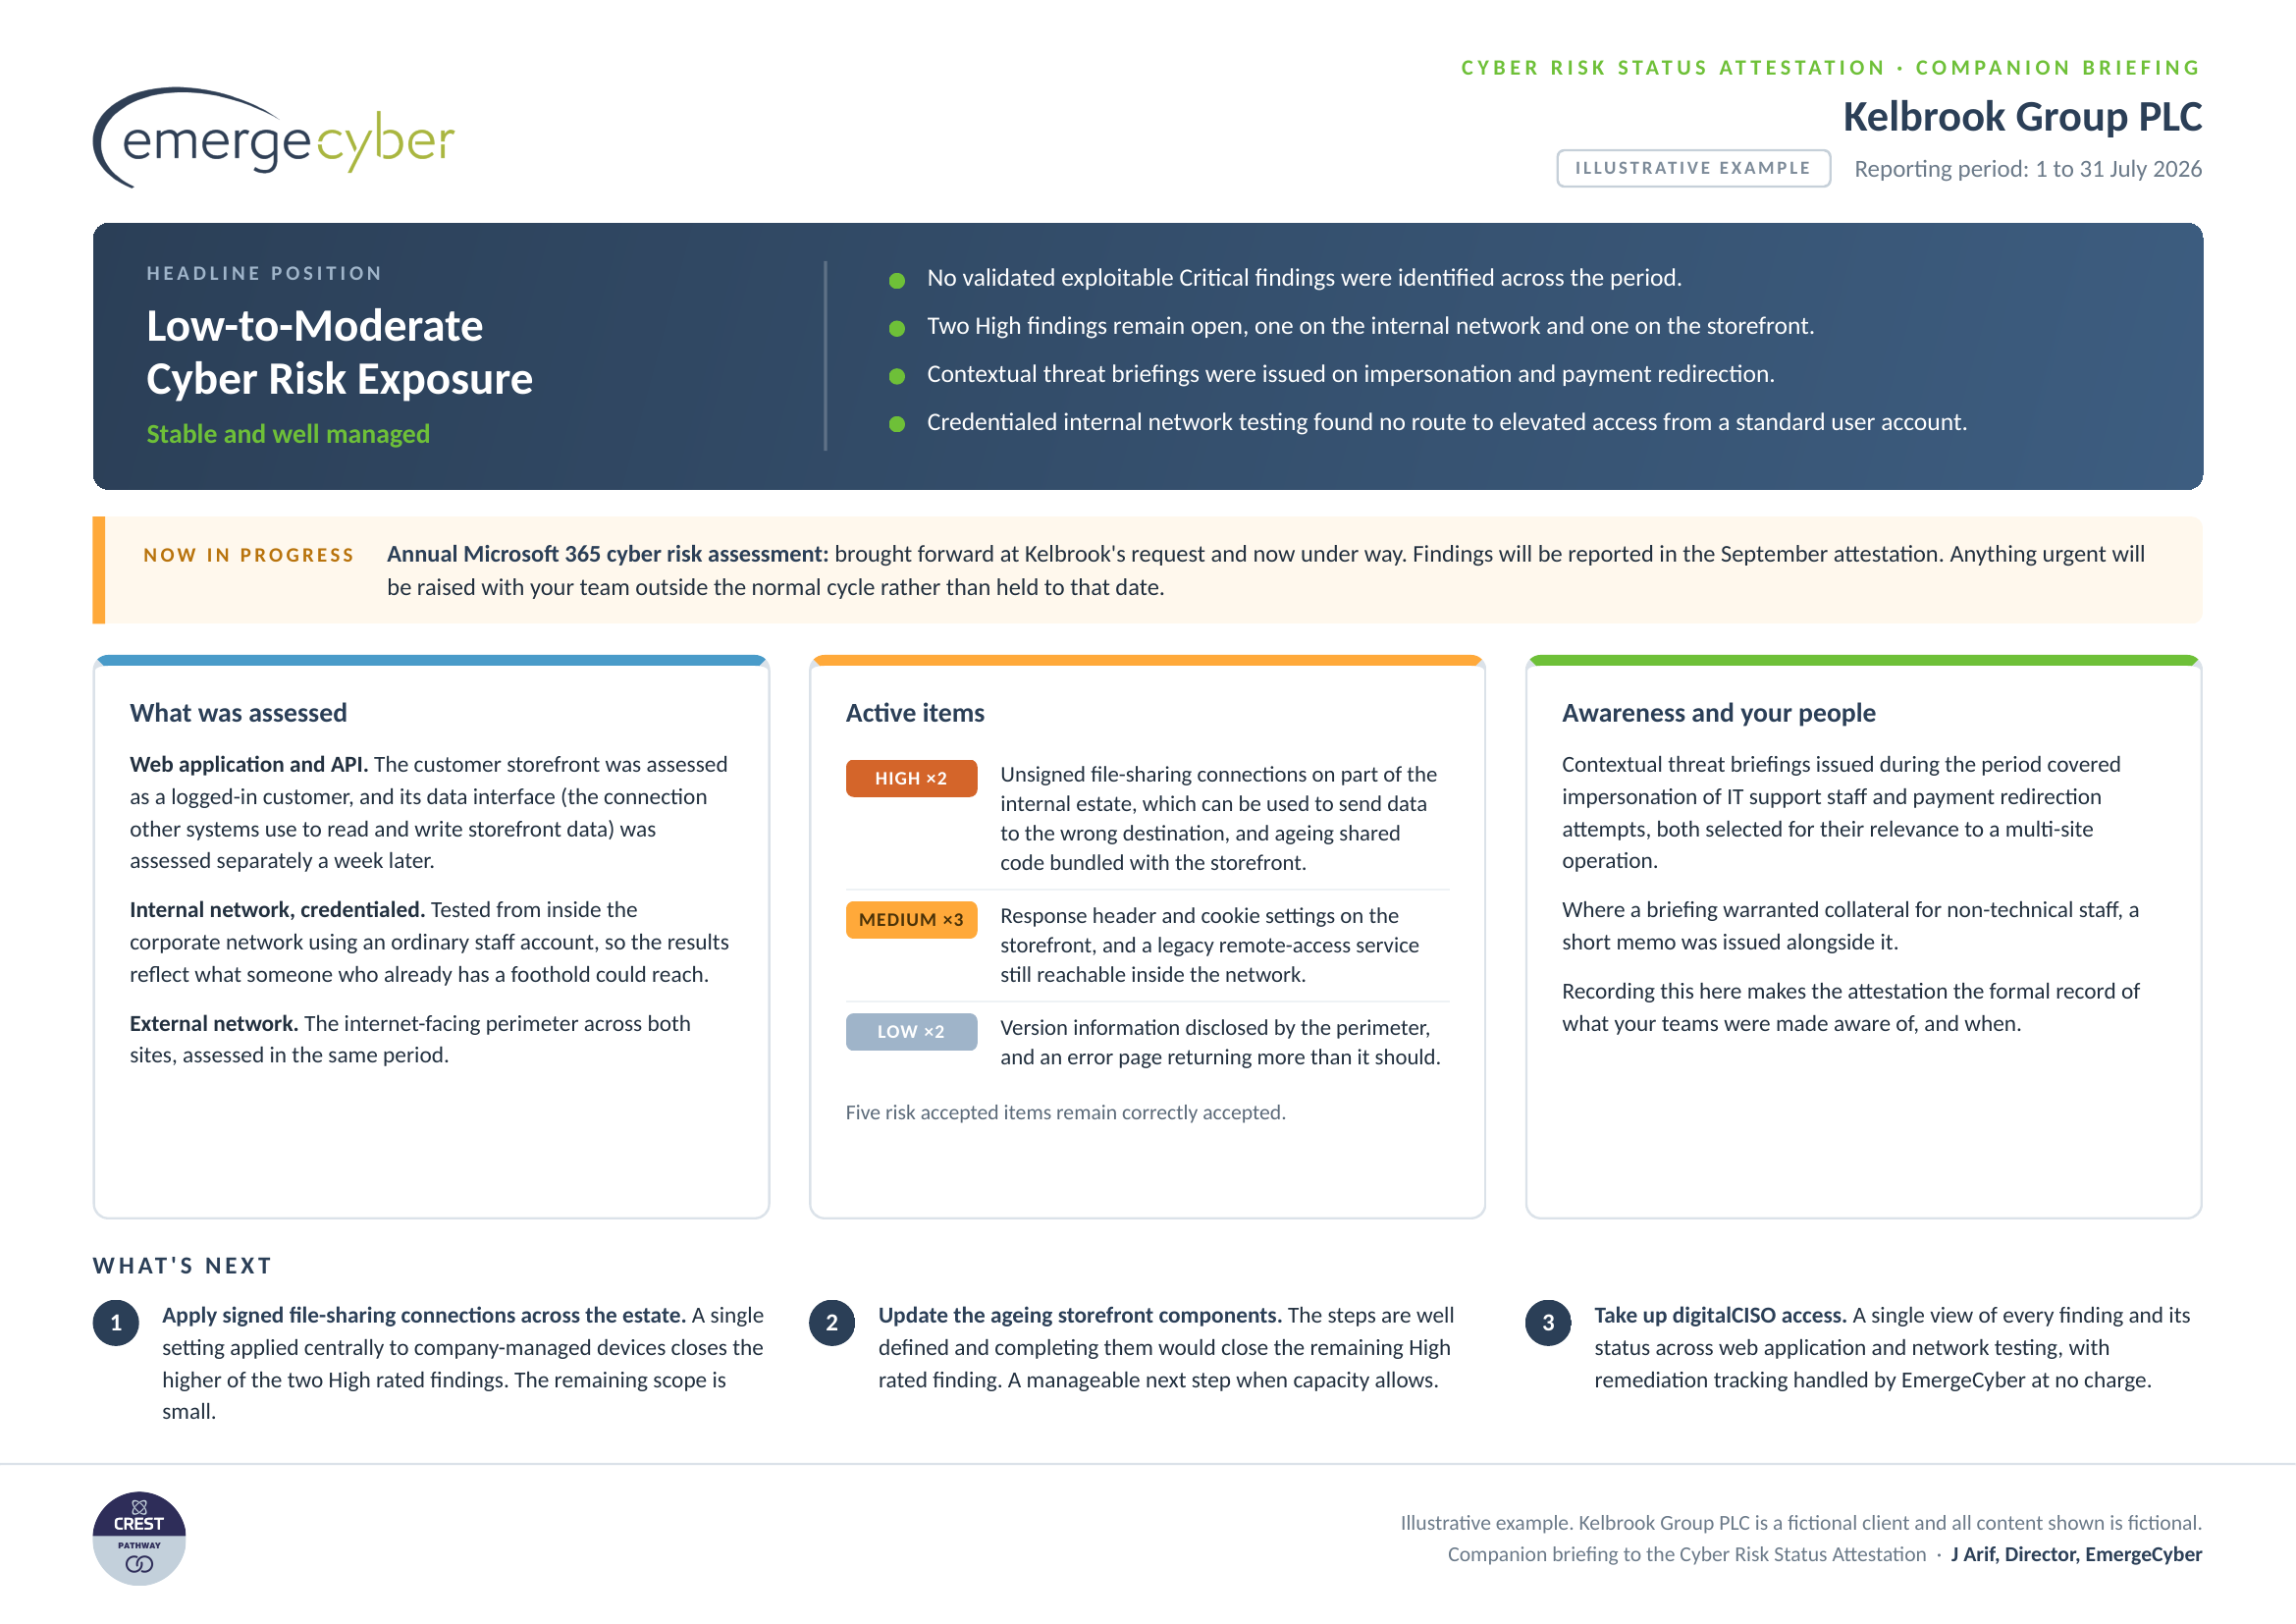
To keep everyone aligned, we produce a Cyber Risk Status Attestation that connects your compliance position with what's actually happening in your environment.
‍
It highlights what matters. What's changed. What needs attention next.

So you're not interpreting risk.

You're acting on it.
An example one-page cyber risk status attestation prepared for a client

A few things worth knowing

What if the framework we need isn't listed?
Do we have to be working towards certification?
Who needs to be involved in the assessment?
How does this work alongside pen testing?
What is the Cyber Risk Status Attestation (CRSA)?
How often is the assessment updated?
What does your risk actually look like today?
You don't need to have all the answers.

We'll help you make sense of where you are.

No jargon. No pressure. Just clarity.
See Where You Stand